DarkBlinders đang vận hành một chiến dịch gián điệp mạng nhắm vào Israel và Khu vực Kurdistan của Iraq bằng các trang đăng nhập giả, dịch vụ lưu trữ đám mây nhái và một ứng dụng họp video giả mang tên StarkMeet. Báo cáo của Dream Research Labs công bố ngày 8/10/2026 cho biết chiến dịch được quan sát từ tháng 8 đến tháng 10/2026 và vẫn hoạt động tại thời điểm công bố.
A Campaign Combining Credential Theft and Malware Installation
DarkBlinders does not rely on a single technique. The group built Outlook Web App pages impersonating Kuwait's Ministry of Foreign Affairs and the Gulf Cooperation Council Secretariat General to collect usernames and passwords. In parallel, Google Drive lookalike domains lured victims into downloading attacker-controlled ZIP files.
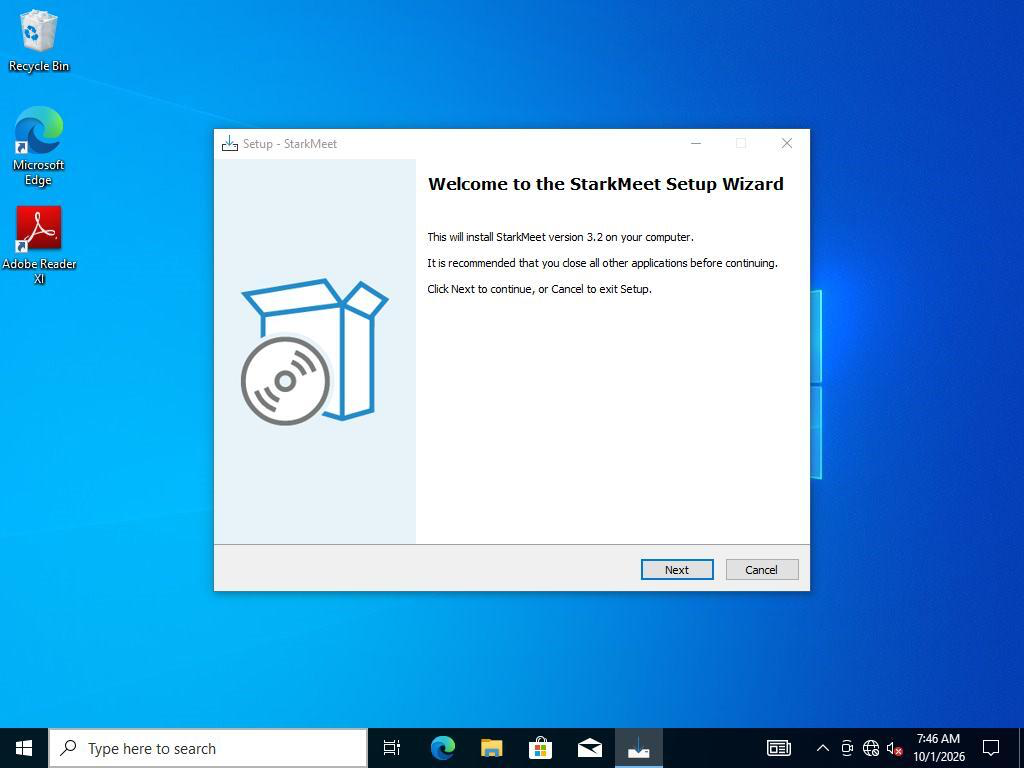
The StarkMeet branch appears to be ordinary online-meeting software. Its installer presents a credible setup interface, while the decoy application offers local camera, microphone, and screen-sharing previews. However, the Join button always returns a fixed error as malicious components are installed separately under a RuntimeBroker directory.
From Infected Host to Selectively Activated Backdoor
The execution chain uses a legitimate signed .NET binary renamed RuntimeBroker.exe to load RuntimeBroker.dll. The malware persists through a Run key in the user's profile and collects system details including machine name, domain, time zone, keyboard layouts, persistence status, and analysis-environment indicators.
Thông tin này được gửi tới kho GitHub myLic dưới tài khoản PeakyBlindersTeam. Nhà điều hành xem xét từng máy trước khi cung cấp vật liệu kích hoạt riêng. Dream quan sát khoảng mười máy đăng ký ban đầu nhưng chỉ hai nạn nhân xuất hiện trong kênh tác vụ giai đoạn hai, cho thấy backdoor được bật có chọn lọc thay vì tự động trên mọi hệ thống.
GitHub Becomes Command-and-Control Infrastructure
RuntimeBroker.dll chứa token truy cập GitHub và đường dẫn tới kho myLic. Một phiên bản lịch sử của tệp Lic.txt còn giữ dữ liệu dùng để tạo khóa AES-256-CBC, cho phép giải mã RuntimeBrokerApi.dll. Thành phần giai đoạn hai được nạp thẳng vào bộ nhớ, giảm khả năng mẫu rõ bị thu thập từ ổ đĩa.
Backdoor sau đó liên lạc với kho myCode bằng token thứ hai, lấy lệnh khoảng 63 giây một lần và gửi kết quả trở lại GitHub. Nó có thể chạy PowerShell trong tiến trình hiện tại, tải lên hoặc tải xuống tệp, tải và giải nén tệp ZIP, đồng thời kiểm tra hạn mức API. Một Cloudflare Worker đóng vai trò kênh chuyển tiếp dự phòng.
A Notable Credential-Rotation Mechanism
To survive token revocation or repository takedown, the malware searches public comments in the Microsoft/vscode repository. A hidden HTML comment block, when correctly structured and successfully decrypted through multiple layers, can provide a new repository owner, repository name, and token. This mechanism turns a trusted public platform into a recovery noticeboard for the command infrastructure.
The use of GitHub does not mean the malicious activity is affiliated with the platform. Abusing a legitimate service lets traffic blend into normal activity while benefiting from HTTPS and highly available infrastructure, thereby increasing the cost of detection and blocking.
Confirmed Victims and Impact
Dream says it confirmed the compromise of a prominent individual in Israel associated with the security sector and a government cloud environment in the Kurdistan Region. Post-compromise activity included credential theft and the exfiltration of at least 1 GB of data from the government cloud environment.
The phishing infrastructure also impersonated diplomatic bodies in Kuwait and the Gulf Cooperation Council, suggesting that intended targeting may extend beyond the confirmed victims. Infrastructure traces indicate intent or preparation, however, and should not be interpreted as proof that every impersonated organization was compromised.
Connections to APT34
Dream assesses with medium-to-high confidence that DarkBlinders belongs to the same activity cluster as UNC5795 and Dust Specter. Shared infrastructure, overlapping victimology, and prior attribution research also suggest, with medium confidence, that this cluster and UNC5187 may be related subclusters within the Iran-linked APT34 ecosystem.
This is an attribution assessment, not an absolute conclusion. Different vendor group names can describe overlapping portions of the same ecosystem, so defenders should prioritize behavior, infrastructure, and technical indicators.
Defensive Signals to Prioritize
- Giám sát tiến trình có tên RuntimeBroker chạy từ
%LOCALAPPDATA%\Microsoft\RuntimeBroker, thay vì vị trí hệ thống Windows thông thường. - Rà soát giá trị
MicrosoftRuntimetrong khóa Run của người dùng và các tiến trình .NET tải System.Management.Automation nhưng không sinh tiến trình powershell.exe. - Analyze unusual periodic access to the GitHub API, especially from workstations with no software-development requirement.
- Check for domains resembling organizational webmail, cloud-storage, or meeting services, and require installation invitations to be verified through an independent channel.
- Revoke sessions, rotate credentials, and inspect cloud data when a fake OWA page is detected, even if the endpoint has not generated a malware alert.
Lessons from the DarkBlinders Campaign
The campaign shows how the line between credential phishing and endpoint compromise is fading. A familiar interface can simultaneously steal accounts, persuade users to run software, and establish long-term persistence. Effective defense therefore requires identity protection, endpoint monitoring, analysis of traffic to code-hosting services, and procedures for verifying meeting invitations.
For government and diplomatic organizations, classifying privileged accounts, restricting long-lived tokens, deploying phishing-resistant authentication, and monitoring bulk data downloads are especially important. Meeting applications delivered outside official distribution channels should be treated as high risk, even when their interfaces appear convincing.
VNCyberS compiled from Dream Research Labs
 Tiếng Việt
 English