
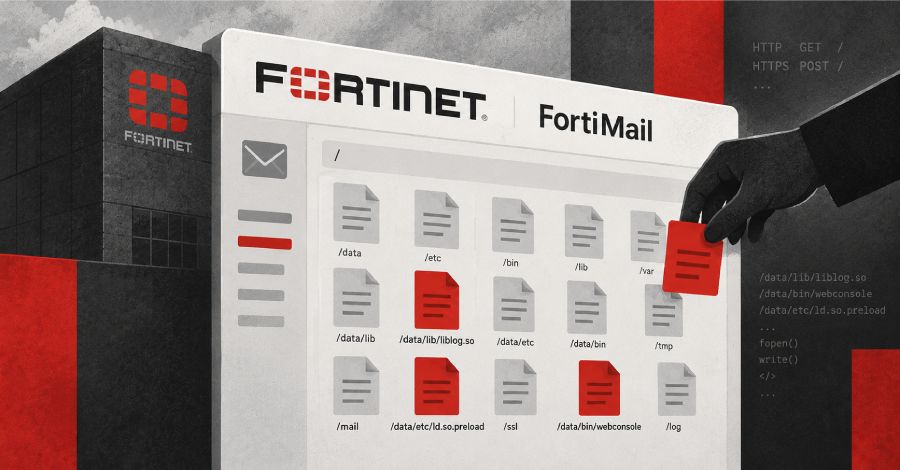
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added CVE-2026-104286, a critical vulnerability in the Fortinet FortiMail email security gateway, to its Known Exploited Vulnerabilities (KEV) catalog. The decision follows evidence of active exploitation. The flaw has a CVSS score of 9.8 and may allow an unauthenticated attacker to write arbitrary files to the system through crafted HTTP or HTTPS requests.
How Dangerous Is CVE-2026-104286?
According to Fortinet's FG-IR-26-175 recommendation, the problem combines two weaknesses: improper path traversal limits (path traversal, CWE-22) and unsafe NULL character handling (CWE-158). A malicious request can bypass the restricted folder and write files to the device without credentials.
The ability to write arbitrary files is particularly critical on an edge device such as an email gateway. If the file is placed in an executable location or loaded by the system service, an attacker can create a springboard to run the code, maintain access, change the configuration, or collect data. Fortinet and CISA have both confirmed mining activity, but have not released the identity of the actor, when the campaign began, or the total number of victims.
Affected FortiMail Versions
The published impact range includes FortiMail 8.0.0-8.0.1, 7.6.0-7.6.6, 7.4.0-7.4.8 and 7.2.0–7.2.9. Branch 7.2 users are recommended to upgrade to branch 7.4 or later. Versions 8.0.2, 7.6.7 and 7.4.9 are listed by Fortinet as bug fixes upon release.
Since patches for some branches are not ready at the time of the warning, administrators should apply mitigation measures immediately. Fortinet recommends disabling the IBE feature with the official configuration command, while disabling Internet access to the administration interface or allowing access only from trusted private networks.
Indicators of Compromise to Review
Fortinet published two IP addresses associated with the attacks: 79.141.169[.]187 and 45.129.0[.]192. Newly added files include /data/lib/liblog.so, /data/bin/webconsole, /data/bin/mailservice and /data/etc/ld.so.preload. The files /bin/smit, /data/etc/httpd.conf and /data/migadmin.tar.gz may have been modified.
Notable log entries include an unusual cron job involving /migadmin, an administrator logout event with an unidentified interface, an IBE decryption error caused by invalid Base64 data, and the creation of an archive account from the command line. An indicator does not conclusively prove compromise, but it should trigger investigation and evidence-preservation procedures.
Why Patching Alone Is Not Enough
Once a vulnerability has been exploited, software updates only block future attacks. The patch does not automatically remove web shells, malicious libraries, unauthorized accounts, or previously created configuration changes. Therefore, the organization must view this as both a gap management task and an incident response situation.
The CISA requires U.S. civilian federal agencies to complete forensic and mitigation analysis by October 4, 2026. While this requirement only applies directly to the U.S. federal sector, any organization operating a public FortiMail should use that timeline as an indicator of urgency.
Recommended Response Process
- Make a list of the entire FortiMail device, determine the version and check which administrative interface is contacting the Internet.
- Restrict admin interface to private network or trusted address list; disable IBE according TO Fortinet's instructions if it cannot be updated.
- Match the IP address, file path, hash value, and log event to the official infiltration indicator.
- If abnormalities are detected, isolate the device, preserve logs and disk images, and review the system each connected to FortiMail.
- Change credentials, API keys, certificates, and secrets that could potentially be exposed; rebuild the device from a trusted source if intrusion is confirmed.
- Install the fixed version as soon as it is available, then continue to monitor traffic and abnormal progress.
Lessons for Email Infrastructure Management
Email gateways typically handle sensitive data and are located at the boundary between the Internet and the intranet. Therefore, an unauthenticated error on the administration interface can produce consequences far beyond the device itself. Segregating the administrative network, restricting access, centrally logging, and preparing the device reconstruction process are the controls required before an incident occurs.
The KEV category helps the organization prioritize according to actual exploitation evidence instead of relying solely on CVSS scores. With CVE-2026-104286, the key message is to simultaneously reduce the attack surface, check for compromised capabilities, and prepare for updates as soon as a suitable patch is released.
VNCyberS compiled from CISA, Fortinet, The Hacker News, and BleepingComputer
















 Tiếng Việt
 English
