
CVE-2026-108186 is a critical flaw in Zoom Workplace for Windows, rated 9.6/10 under CVSS 3.1. An attacker needs no account or existing privileges, although user interaction is still required to complete the attack chain.
What vulnerability was disclosed?
On November 10, 2026, Zoom published bulletin ZSB-26023 for an improper input validation issue, tracked as CVE-2026-108186 and mapped to CWE-20. It affects Zoom Workplace for Windows from version 7.1.0 up to, but not including, 7.1.8.
Why is the CVSS score 9.6?
Vector CVSS AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:H/A:H indicates network reachability, low complexity, no privileges required, and high potential impact on confidentiality, integrity, and availability. The UI:R value means user interaction remains necessary, so “unauthenticated” does not mean the victim plays no role.
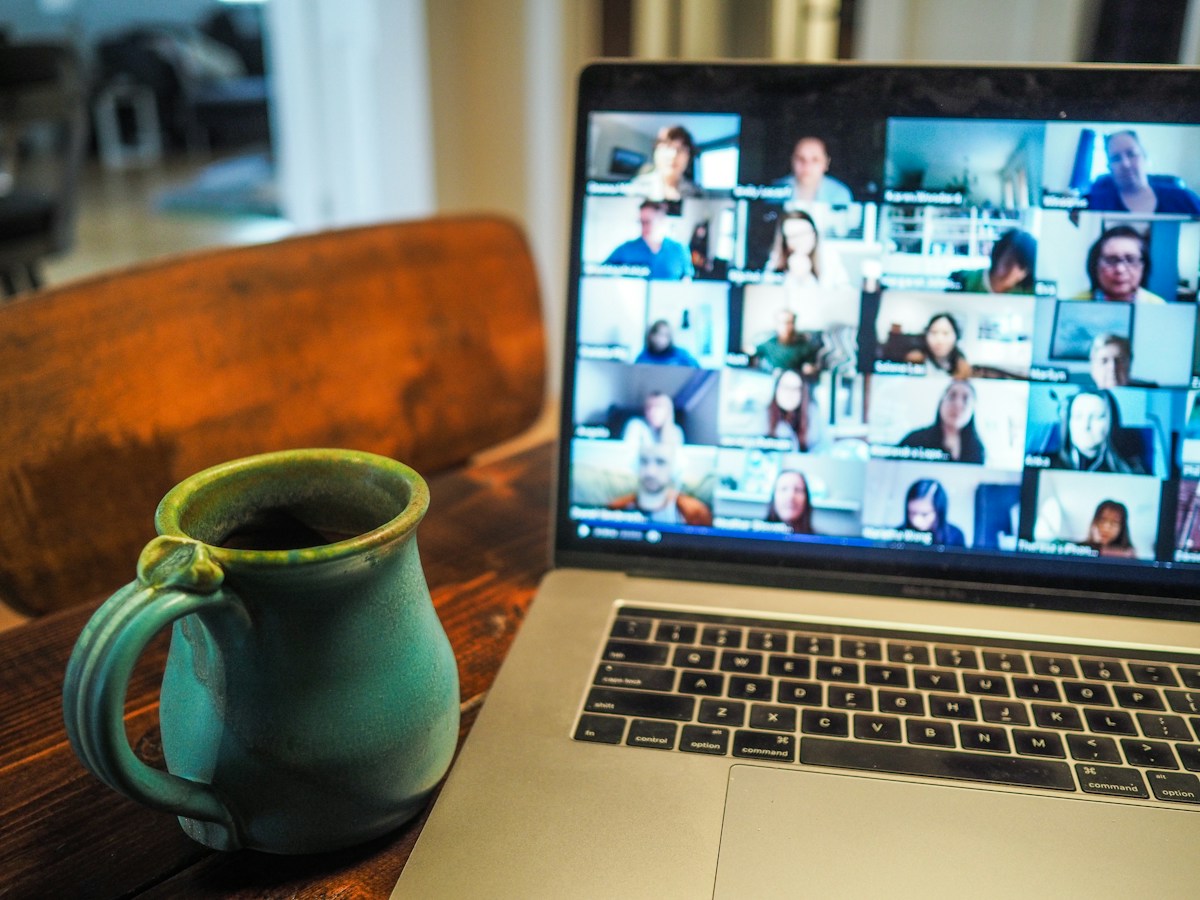
What does remote privilege escalation mean?
Privilege escalation occurs when low-privileged code or a user gains capabilities beyond those intended. Zoom and the CVE record only confirm network-based exploitation; neither public exploit code nor reproduction-level technical details were disclosed. Organizations should avoid inventing a mechanism but treat the issue as an urgent endpoint risk.
Which systems are affected?
The confirmed scope is Zoom Workplace for Windows 7.1.0 through versions earlier than 7.1.8. macOS, Linux, iOS, and Android are not listed as affected. Administrators should inventory deployed versions rather than relying solely on auto-update policy.
Is there evidence of exploitation?
CISA enrichment dated November 11 marked exploitation as “none,” meaning no confirmed exploitation evidence at assessment time. This is not a guarantee of safety: researchers and threat actors commonly analyze patches immediately after disclosure.
What should users do now?
- Update Zoom Workplace for Windows to 7.1.8 or later from the official Download Center.
- Check the installed version and confirm that updating completed.
- Avoid suspicious meeting links, files, and content from unknown sources.
- Restart the application after updating when organizational procedures require it.
How should enterprises respond?
IT teams should query every Windows endpoint, prioritize systems with administrative access or sensitive data, and enforce version 7.1.8 as the minimum. Review EDR, proxy, and email telemetry for unusual chains involving meeting invitations or child processes, validating findings with evidence rather than assumptions.
Security lessons from CVE-2026-108186
Collaboration tools are installed on most endpoints and therefore offer attackers a valuable target. Centralized version control, reduced local privileges, access segmentation, and process monitoring provide durable defenses. Fast patching fixes this flaw; privilege management and visibility reduce the impact of the next one.
VNCyberS compiled from Zoom Security Bulletin, NVD, CISA, and The Hacker News







 Tiếng Việt
 English
